Identity and access
Administrator groups and roles
Administrator rights can follow a directory group, so removing someone from the group removes their admin access.
What it is
Administrator rights can come from a bootstrap email list, an explicit grant in People, or membership in an IdP group. Roles are user, team lead and administrator.
Why you want it
Admin access should follow the directory too. Mapping an IdP group to the admin role means removing someone from that group removes their admin rights at the next sign-in.
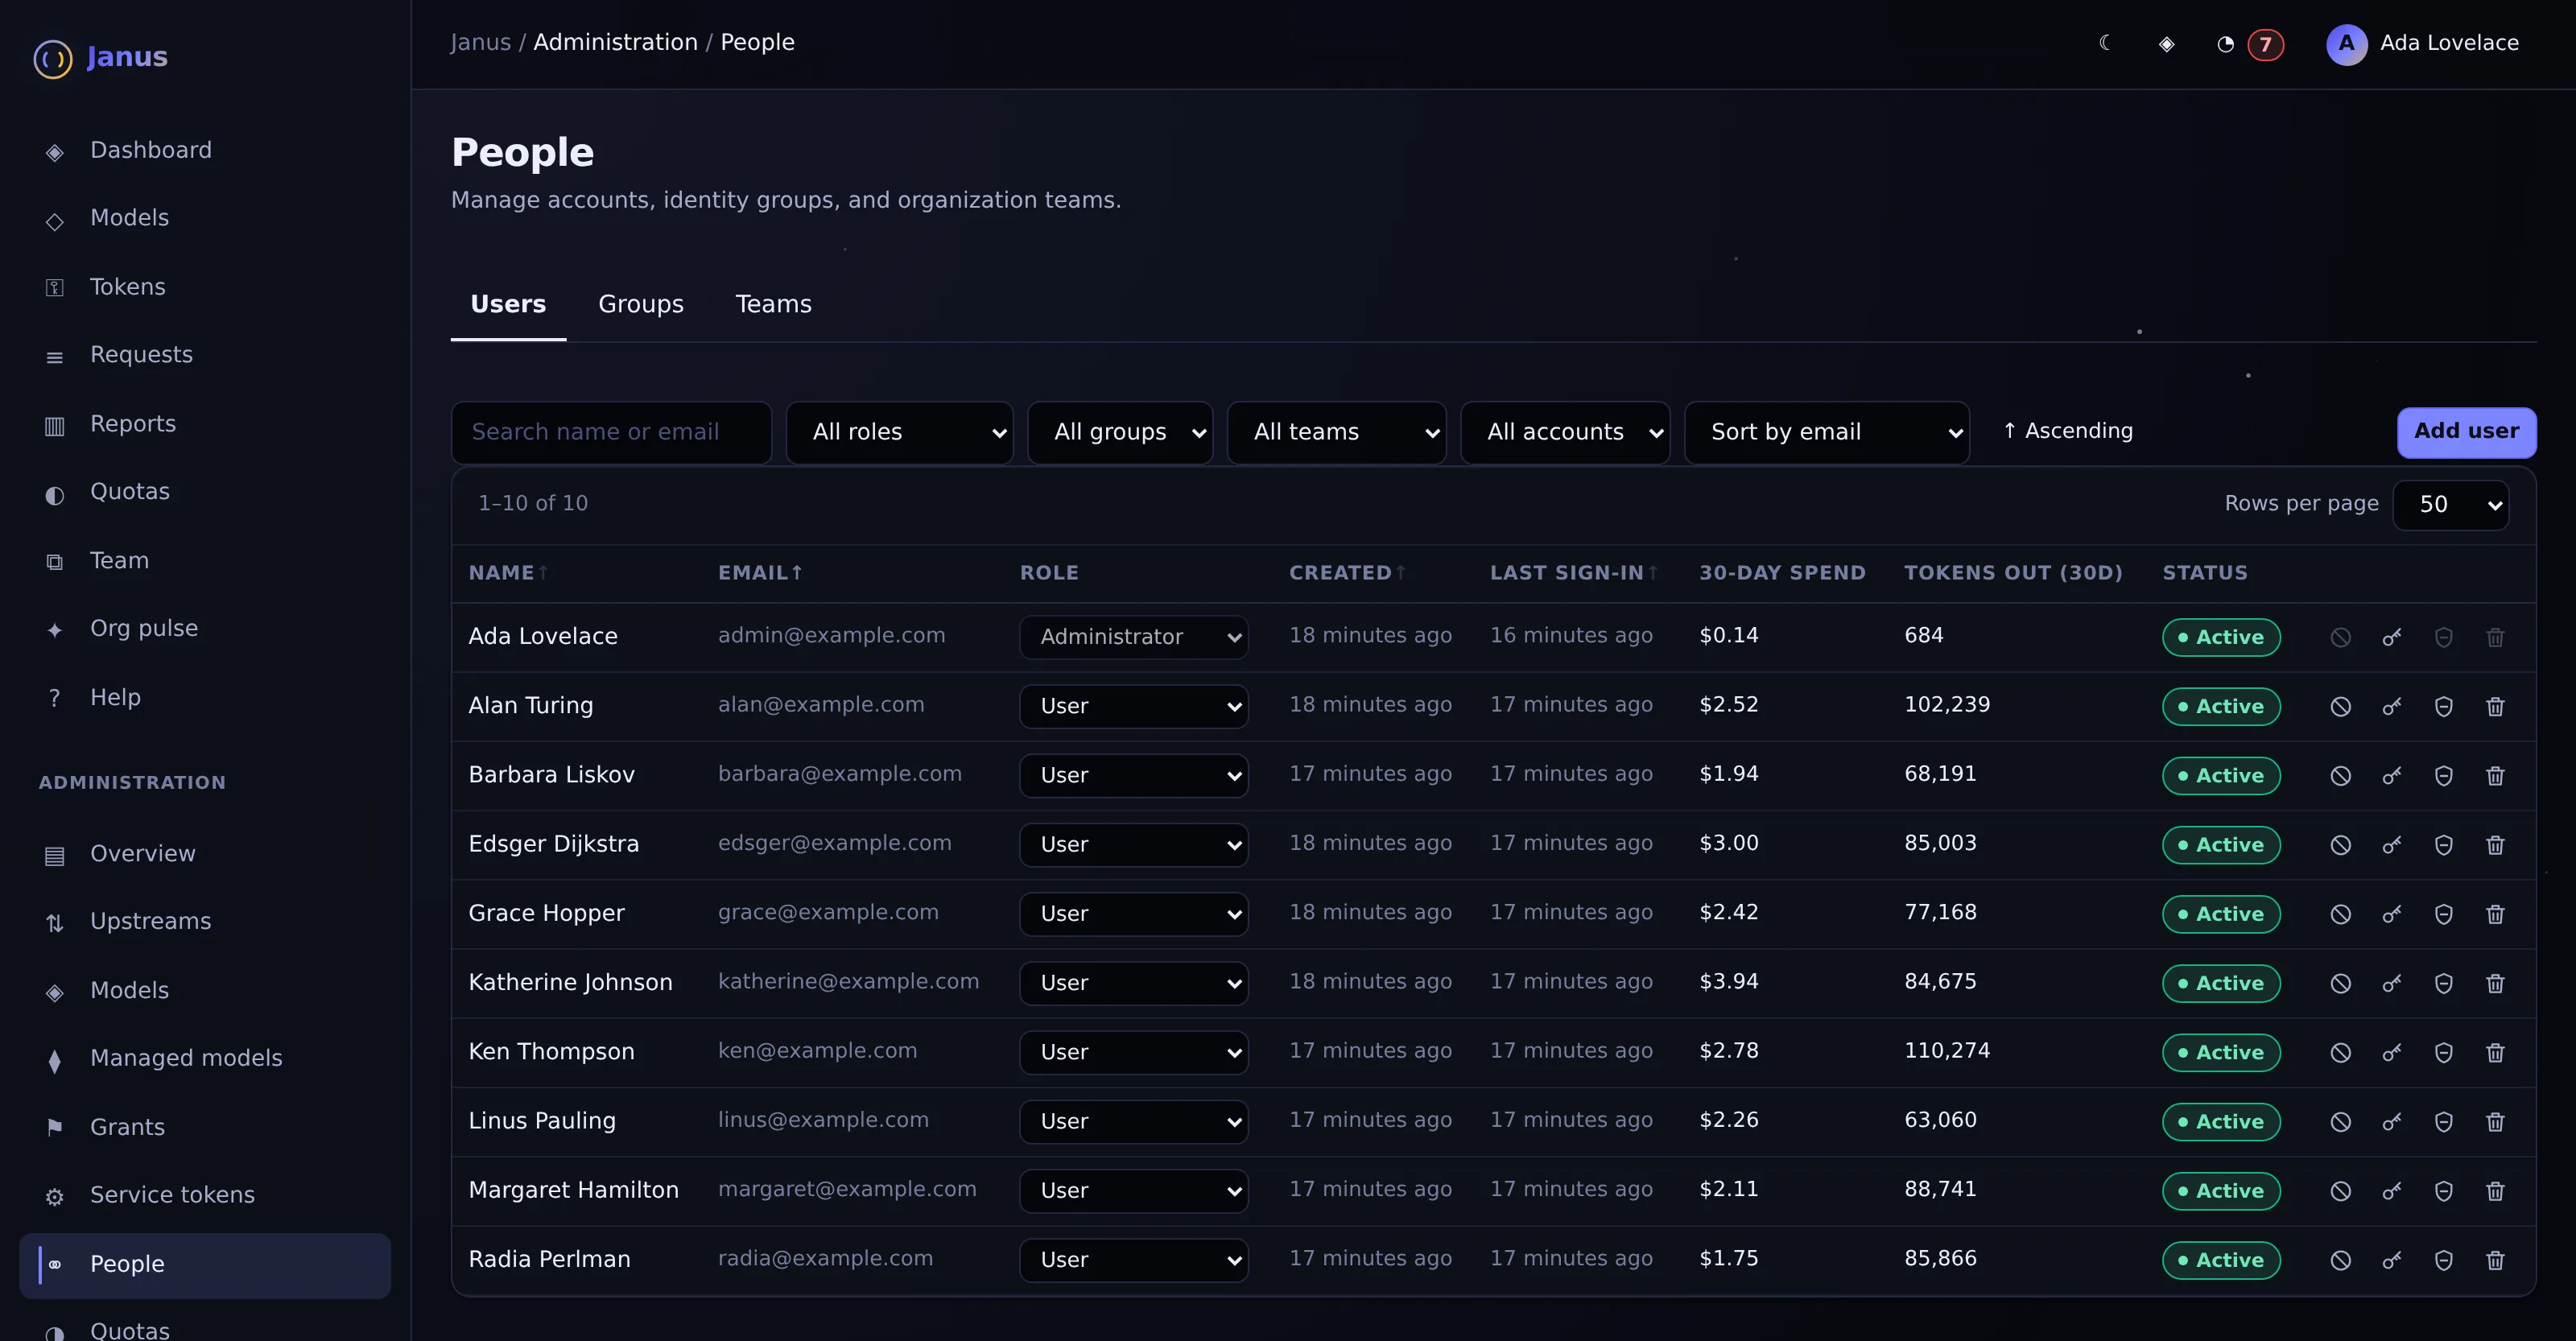
Everyone with access, their role, last sign-in, 30-day spend and status.
Actual Janus interface · Demo identities and synthetic usageHow it works
- Three independent sources combined with OR, so withdrawing one never collapses the others
- Admin groups editable in the UI or via JANUS_ADMIN_GROUPS (environment entries are read-only failsafes)
- Group-based admin is re-evaluated on every sign-in
- Janus refuses to demote or disable the last active administrator
In the product
Screenshot above. Actual Janus interface with demo identities and synthetic usage.
See it on your own network.
The Community edition is free for up to 25 people. The 30-day Business trial unlocks every Business feature.