Identity and access
Request policy rules
Block an unapproved tool or an untrusted network before the request reaches a provider or costs anything.
What it is
Block requests by user agent, source IP, forwarded-for chain, path, method, header, token prefix or model, combined with AND, OR and NOT. Rules run before the request reaches a provider.
Why you want it
Stop an unapproved tool or a script from a network you don't trust before it costs anything. Rules are a policy control, and the UI says plainly that client signals can be spoofed.
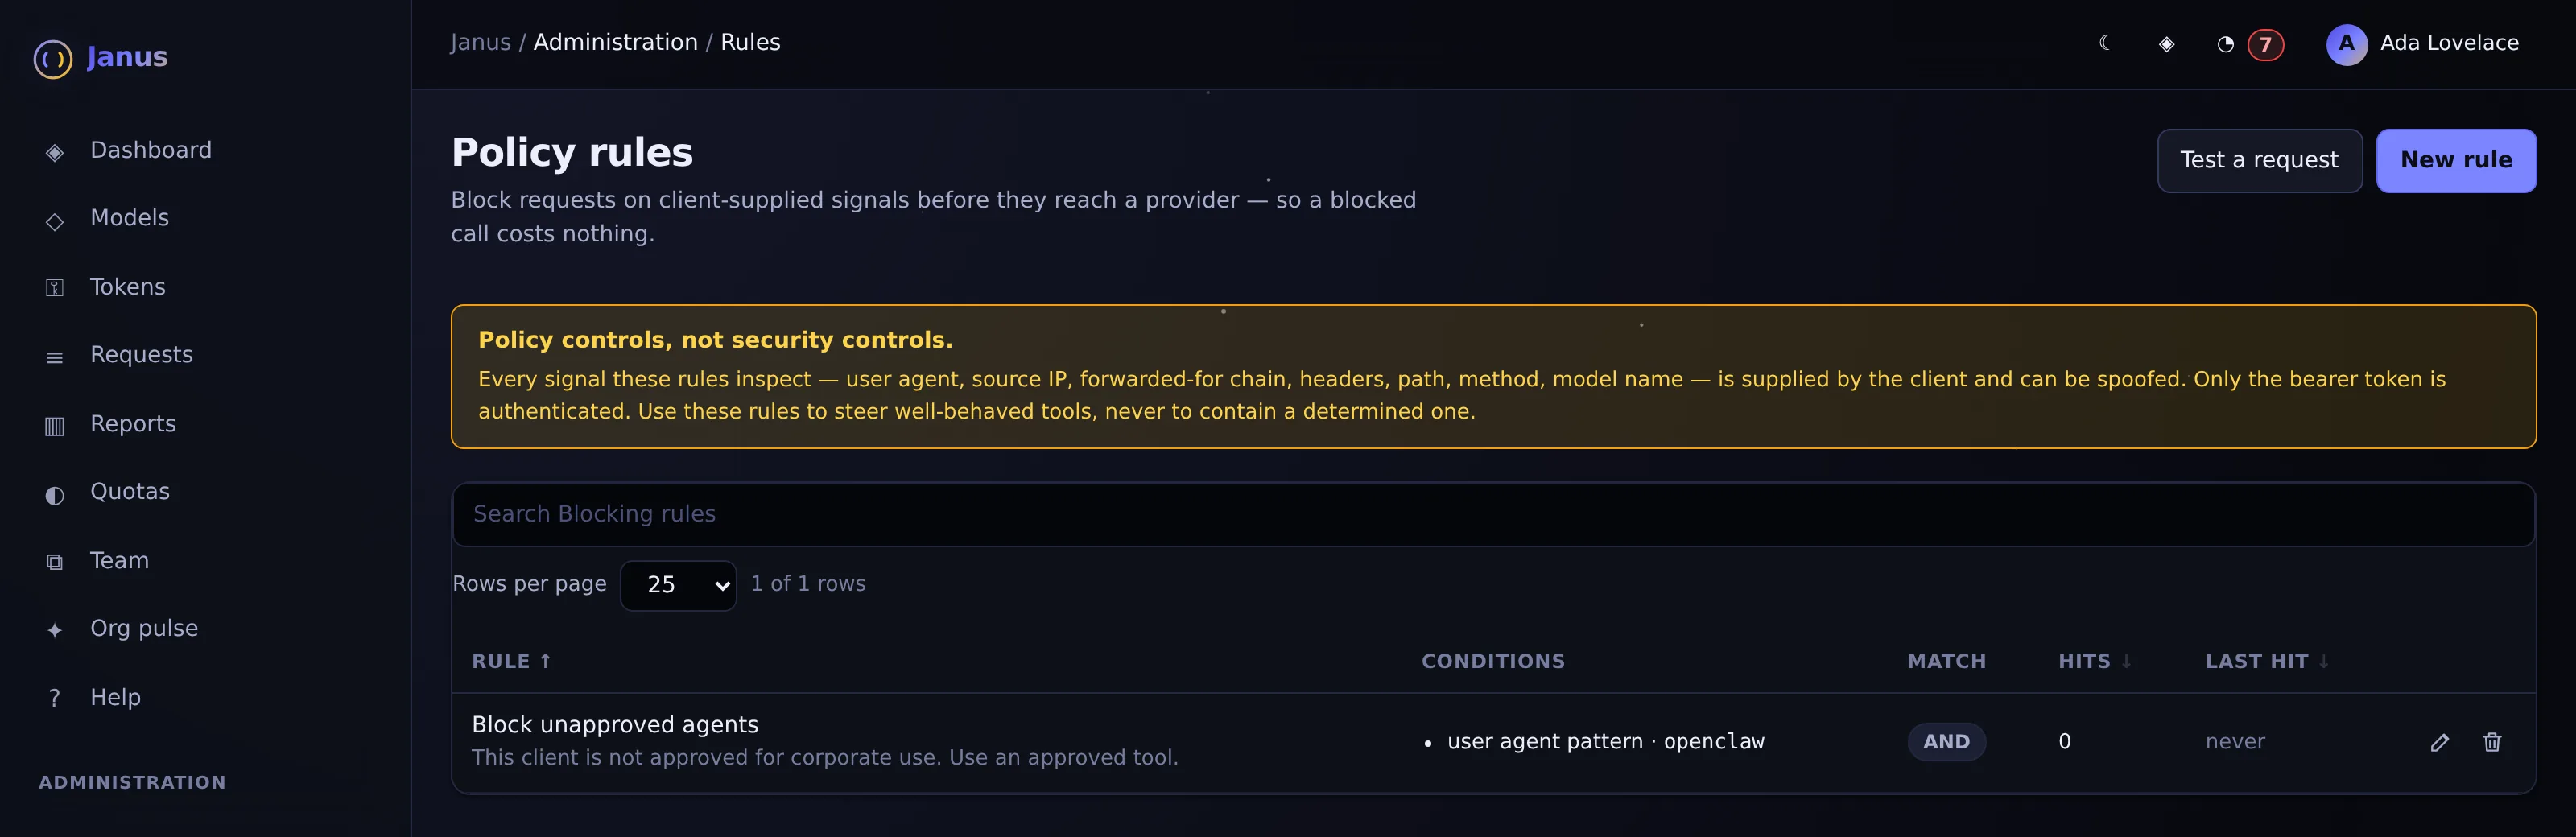
Request rules with hit counts, here blocking an unapproved AI agent by its user agent.
Actual Janus interface · Demo identities and synthetic usageHow it works
- Eight request signals
- Clauses composed with and/or/not; first matching enabled rule blocks
- Hit counts and last-hit time shown per rule
- Evaluated on ingress, so blocked traffic is never billed
In the product
Screenshot above. Actual Janus interface with demo identities and synthetic usage.
See it on your own network.
The Community edition is free for up to 25 people. The 30-day Business trial unlocks every Business feature.