Identity and access
SCIM 2.0 provisioning
Your identity provider pushes people and groups to Janus, and leavers lose access, keys and sessions at once.
What it is
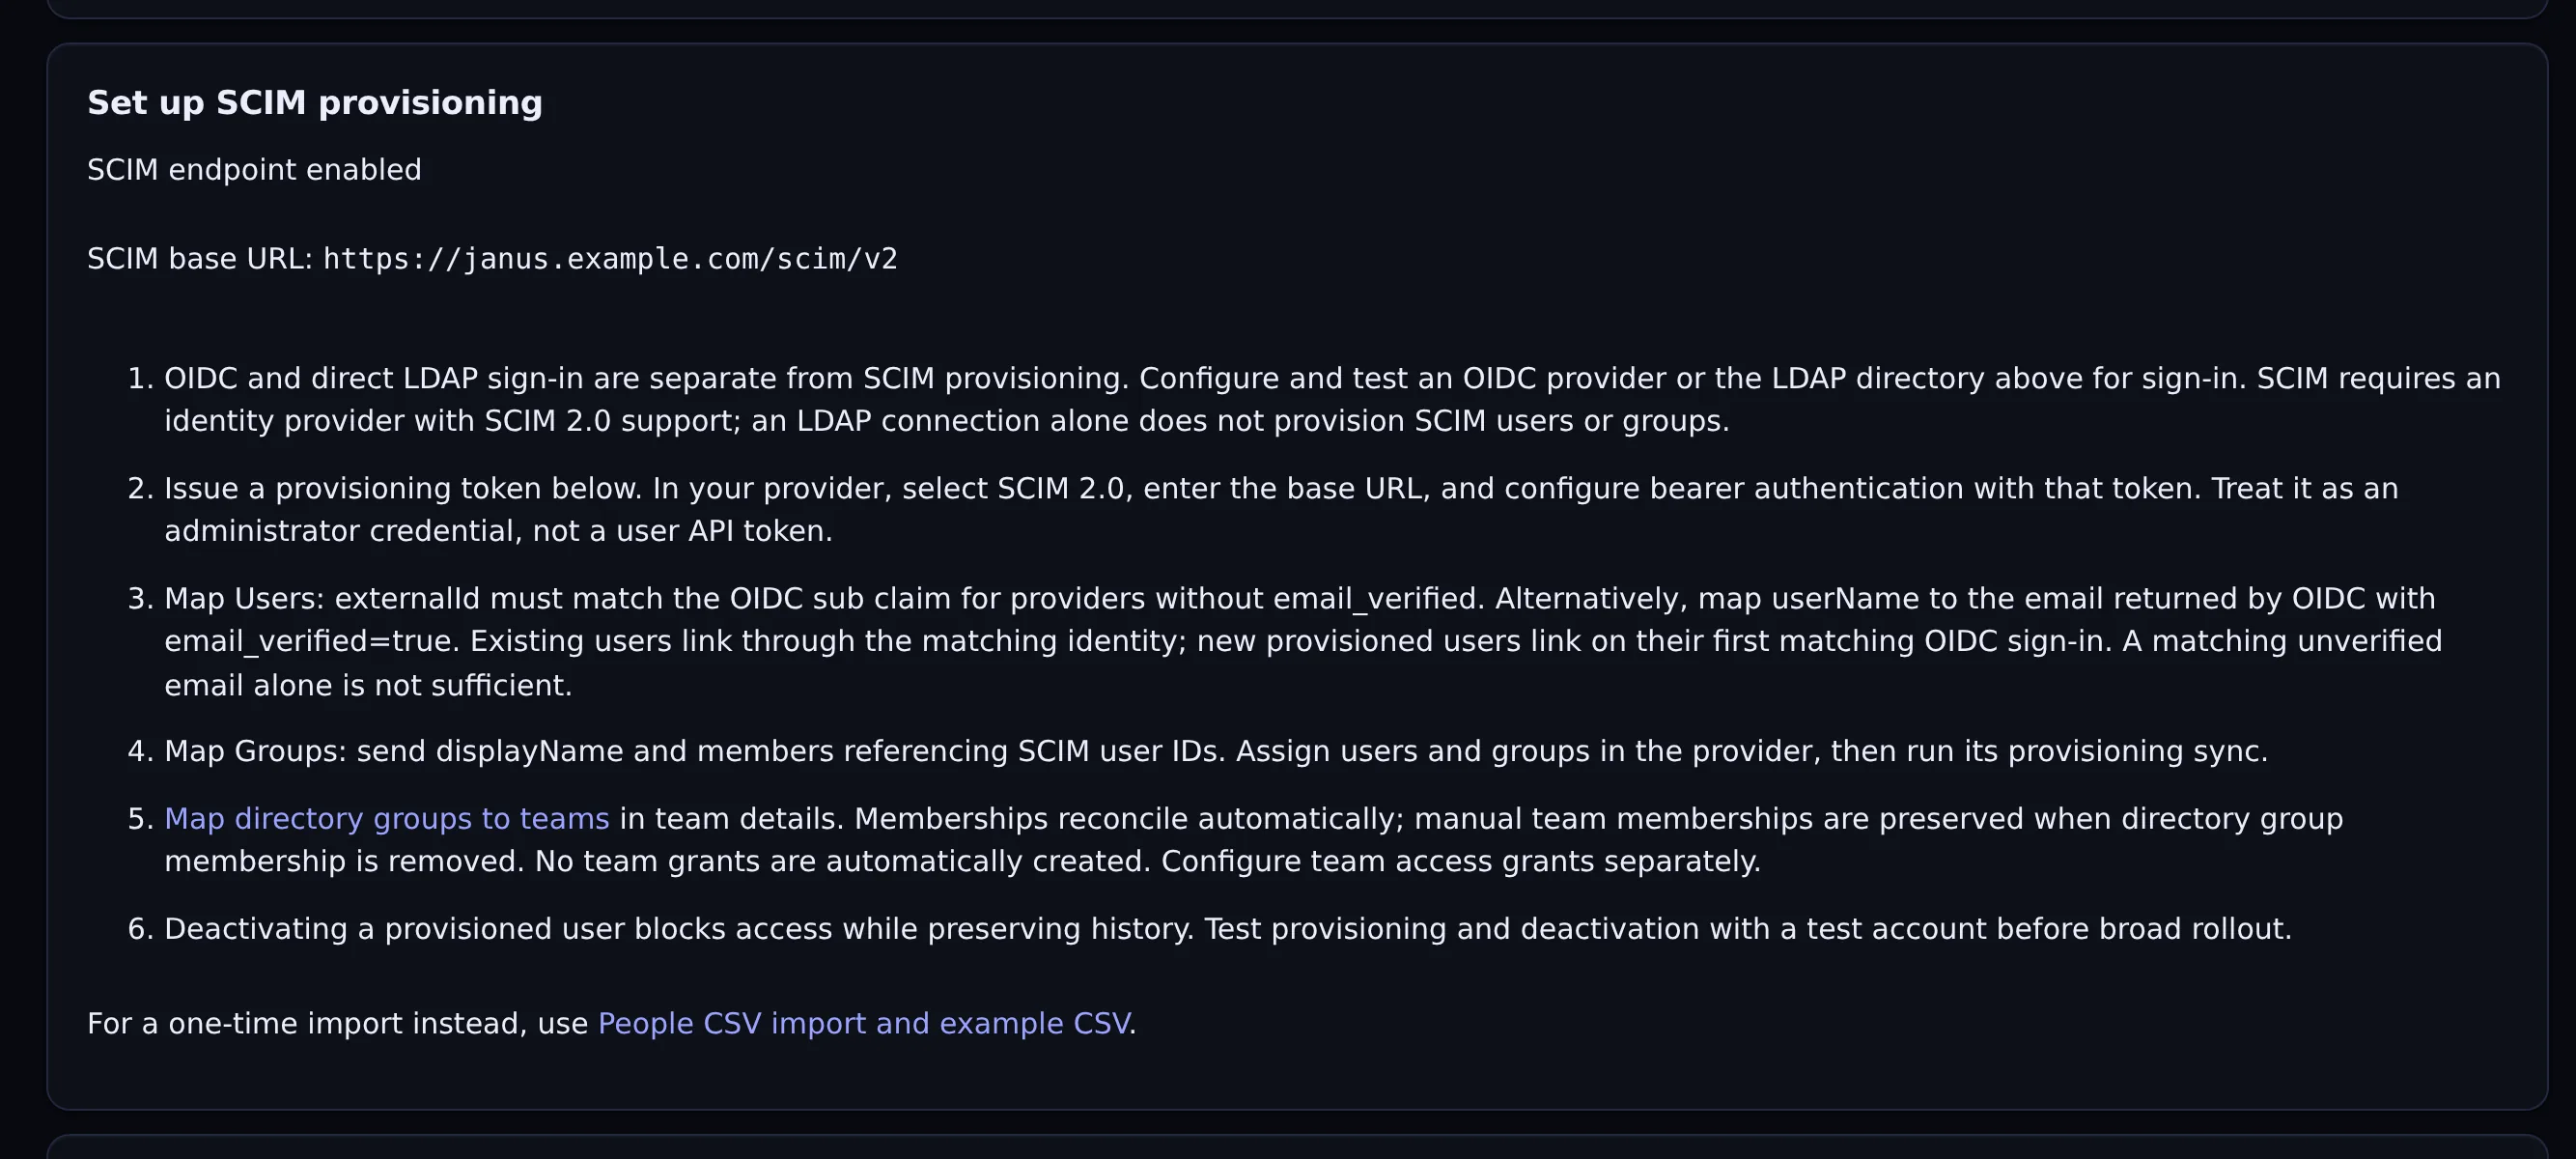
Your identity provider pushes users and groups to Janus over SCIM 2.0. Deprovisioning a person disables them, revokes their API keys and ends their sessions.
Why you want it
Offboarding has to be immediate and complete. SCIM removes the gap between someone leaving in the directory and their AI access actually ending.
How it works
- Base URL /scim/v2 with Users, Groups, ServiceProviderConfig, Schemas and ResourceTypes
- PATCH and filtering supported (eq, co, sw, and/or/not, value paths); bulk, sort and ETag are not
- Dedicated bearer credentials with optional expiry, atomic rotation and revocation
- SCIM groups can be mapped to teams; deactivation withdraws team membership sources
See it on your own network.
The Community edition is free for up to 25 people. The 30-day Business trial unlocks every Business feature.