Security gateway
Secret detection and redaction
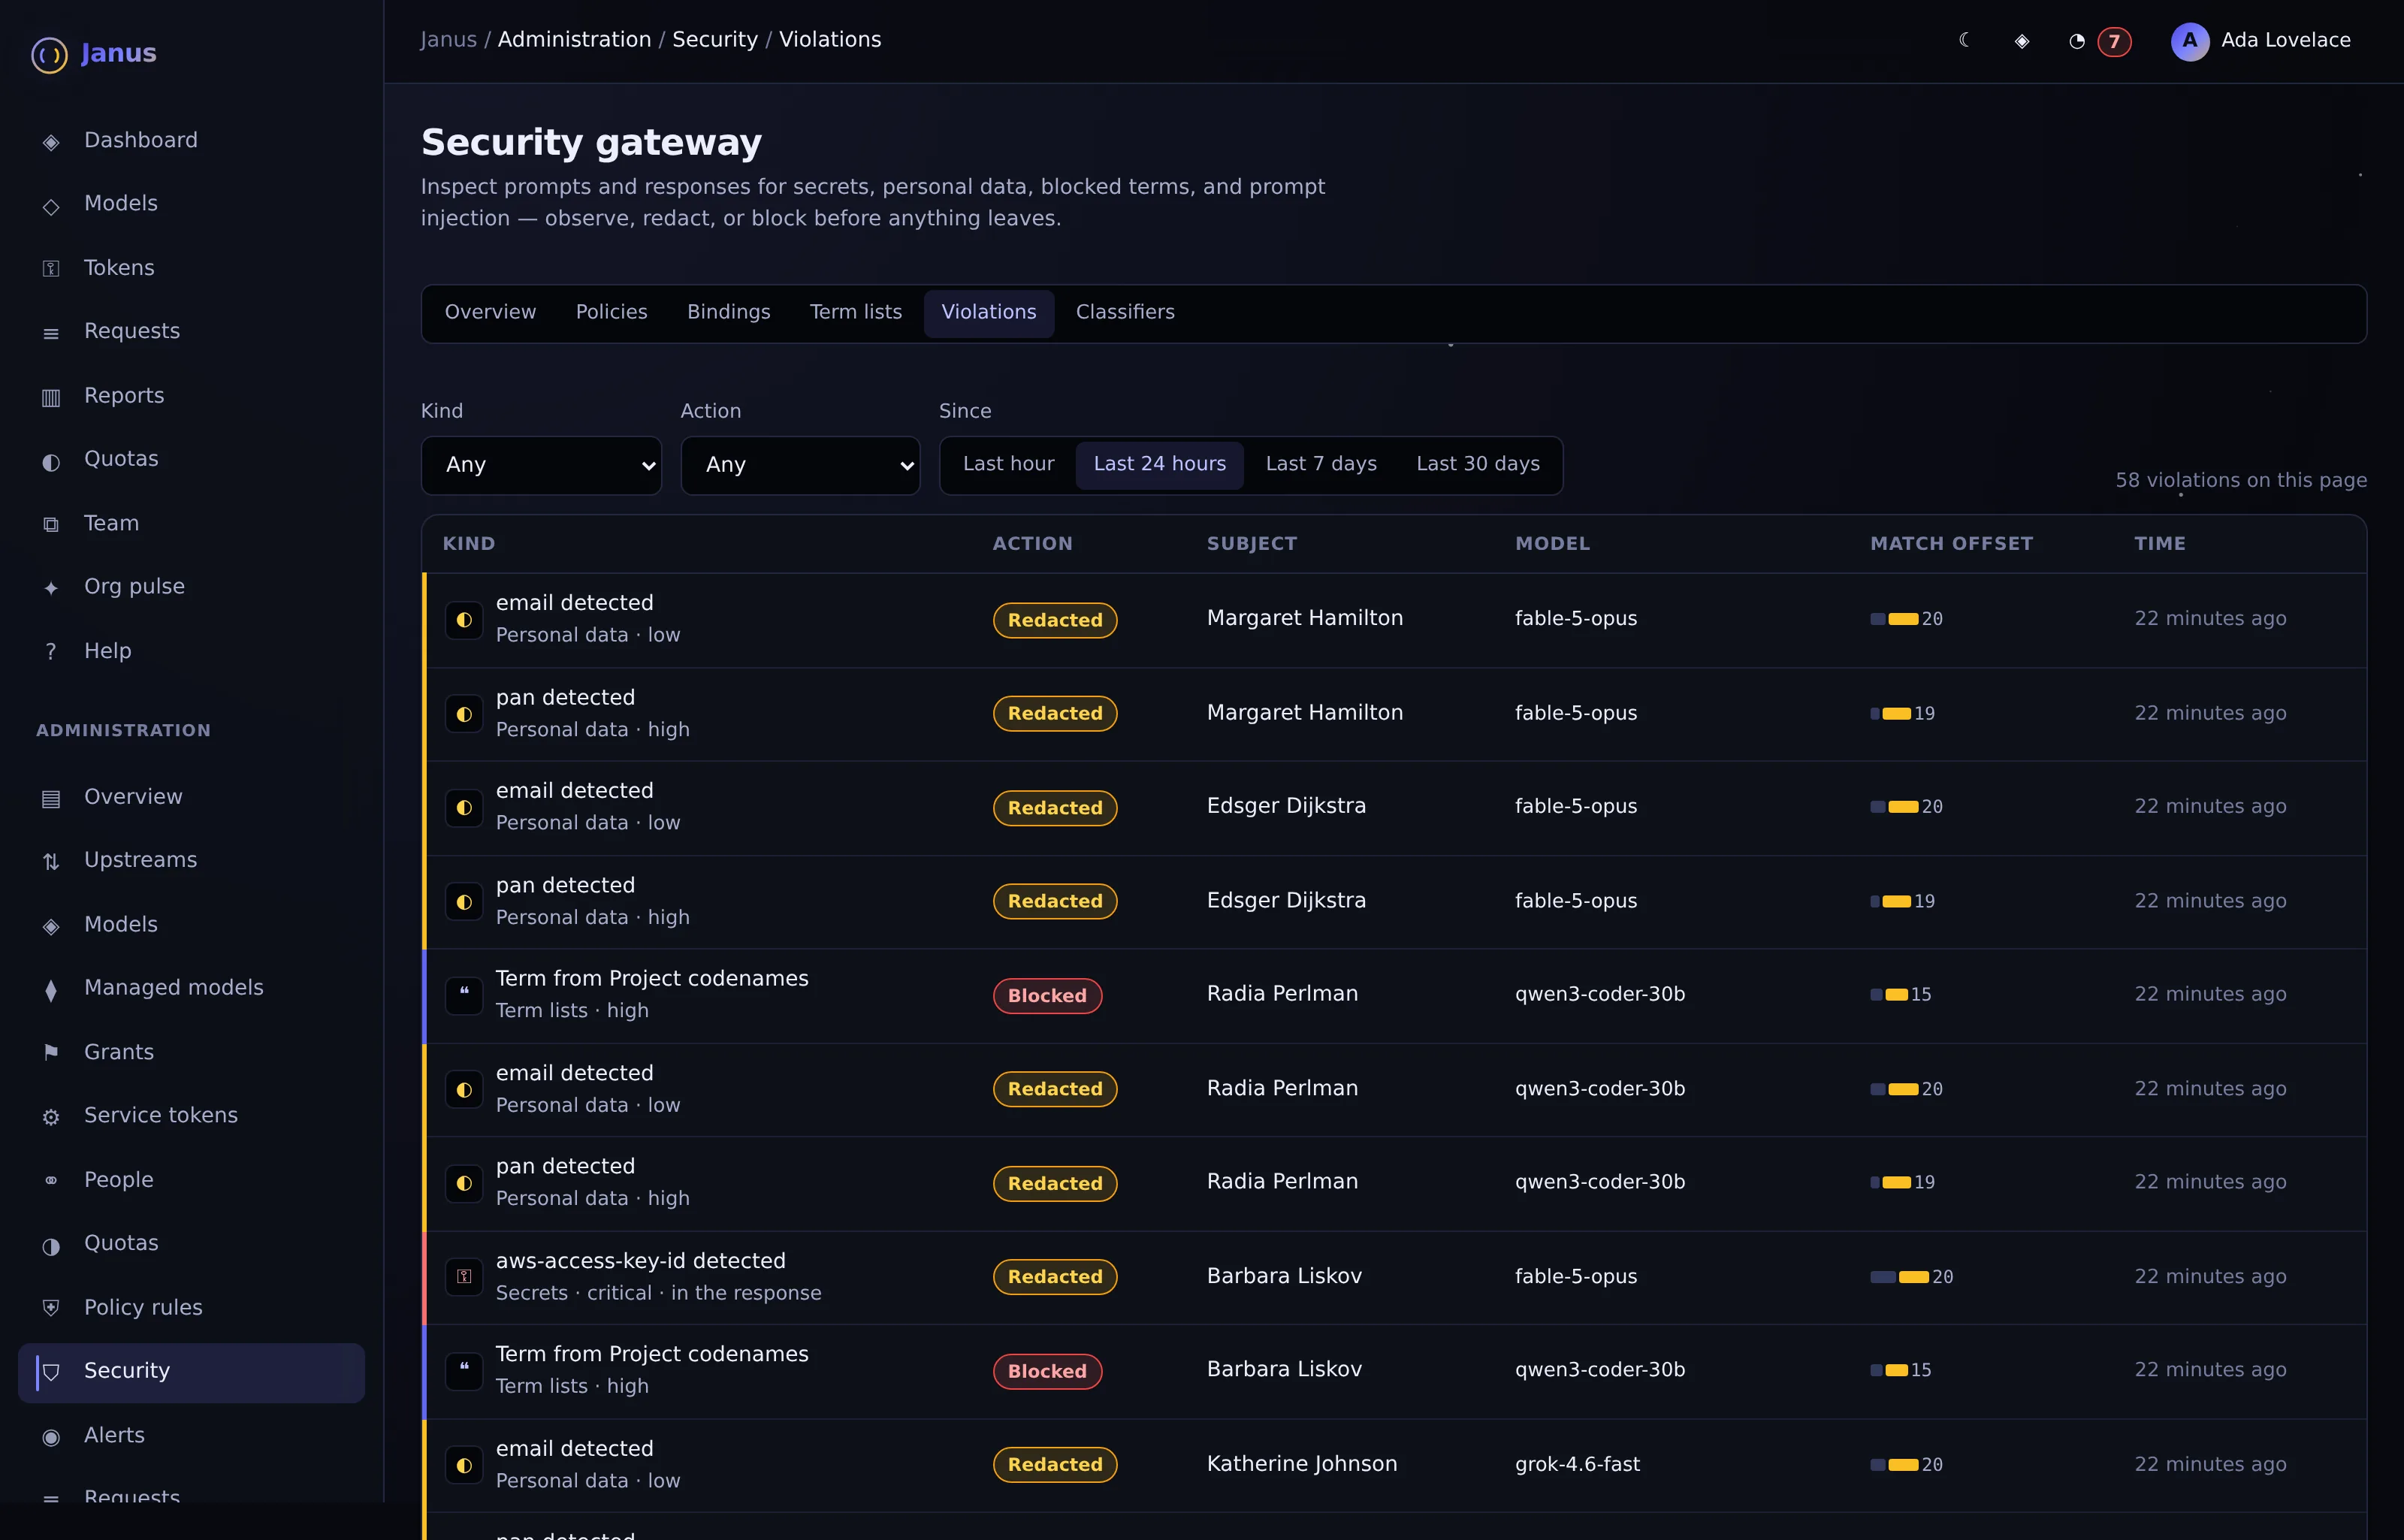
Twenty-seven detectors catch API keys, cloud credentials and passwords, then redact them or block the request.
What it is
Built-in detectors catch API keys, cloud credentials, private keys, tokens and passwords in prompts. Each rule can observe, redact the secret before it leaves, or block the request with a reason.
Why you want it
People paste config files and logs into chat. Catching credentials at the gateway stops them from landing in a provider's logs.
How it works
- 27 bundled rules including AWS, GCP, Azure, GitHub, GitLab, Slack, Stripe, OpenAI, Anthropic, private keys, JWTs and connection strings
- Runs inside the gateway with no external service
- Also applies to responses, including streams
See it on your own network.
The Community edition is free for up to 25 people. The 30-day Business trial unlocks every Business feature.